AWS Direct Connect vs Site-to-Site VPN — Complete Networking Guide
Understand the differences between AWS Direct Connect and Site-to-Site VPN with real-world use cases, performance comparison, and best practices for hybrid cloud networking.
AWS Direct Connect vs Site-to-Site VPN — Complete Guide
When connecting your on-premise data center to AWS, two major options are available:
- Site-to-Site VPN
- AWS Direct Connect
Both enable hybrid cloud connectivity, but they differ significantly in performance, cost, and reliability.
Let’s break them down clearly.
What is Site-to-Site VPN?
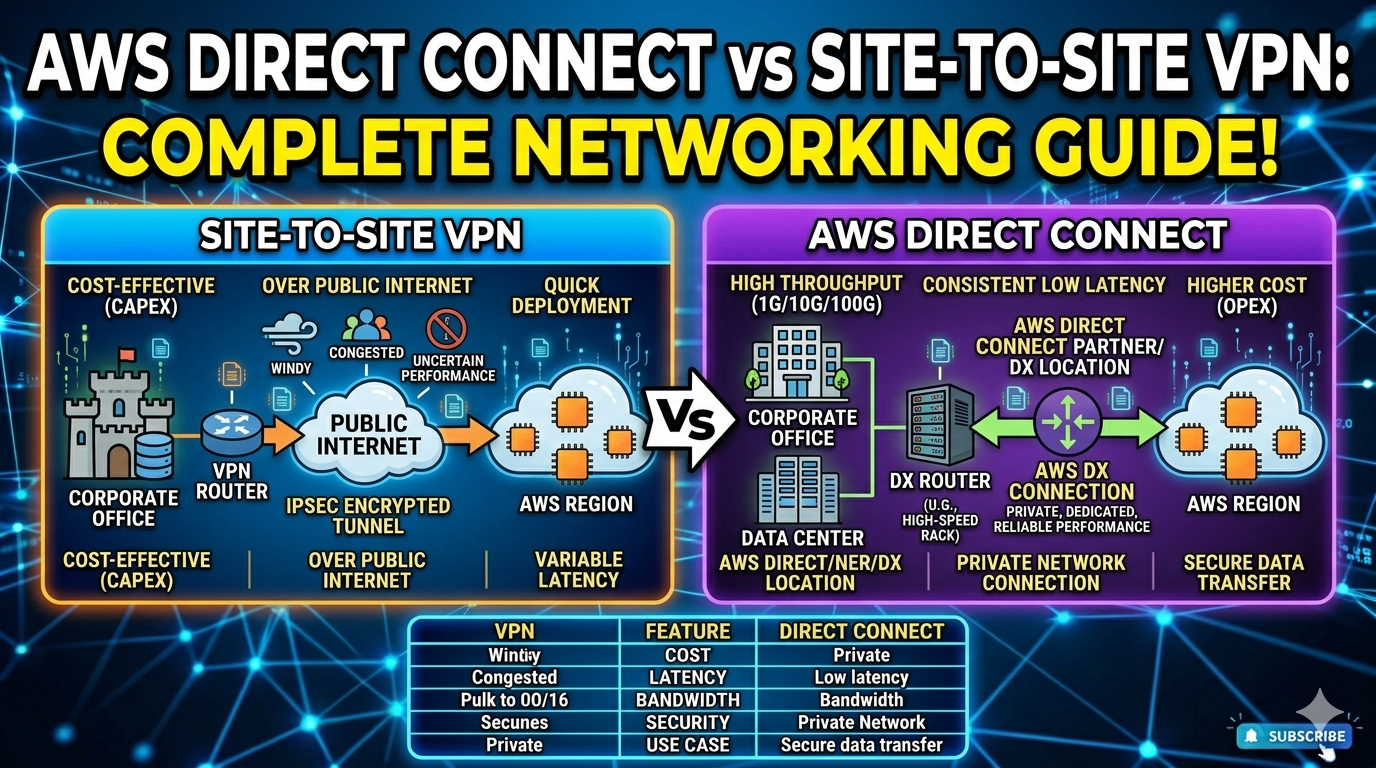
A Site-to-Site VPN creates a secure, encrypted connection between your on-premise network and your AWS VPC over the public internet.
Key Idea:
Secure tunnel over the internet.
On-Premise ↔ Internet ↔ AWS VPC
What is AWS Direct Connect?
AWS Direct Connect is a dedicated private network connection from your data center to AWS.
Key Idea:
Private, high-speed, and consistent connection.
On-Premise ↔ Direct Connect ↔ AWS VPC
Key Differences
| Feature | Site-to-Site VPN | AWS Direct Connect |
|---|---|---|
| Connection Type | Internet-based | Private dedicated line |
| Security | Encrypted (IPSec) | Private + optional encryption |
| Performance | Variable | Consistent, high-speed |
| Latency | Higher | Lower |
| Cost | Low | High |
| Setup Time | Quick | Longer (requires setup) |
| Reliability | Depends on internet | Highly reliable |
Real-world Example
Scenario:
You have:
- On-premise office
- AWS infrastructure
Using VPN:
- Quick setup
- Good for testing or small workloads
Using Direct Connect:
- Ideal for production
- High data transfer
- Stable performance
When to Use What?
Use Site-to-Site VPN when:
- You need quick setup
- Budget is limited
- Workloads are small or temporary
Use Direct Connect when:
- You need high bandwidth
- Low latency is critical
- Running production systems
- Large data transfer (e.g., backups, analytics)
Hybrid Approach (Best Practice)
Many companies use both:
- Direct Connect → Primary connection
- VPN → Backup (failover)
This ensures high availability.
Advantages Summary
Site-to-Site VPN:
- Easy to set up
- Cost-effective
- Secure
Direct Connect:
- High performance
- Predictable latency
- Reliable
Simple Analogy
Think of connectivity like travel:
- VPN → Public highway (can be traffic)
- Direct Connect → Private express lane (fast & dedicated)
Final Thoughts
- VPN is best for quick, low-cost setups
- Direct Connect is best for enterprise-grade systems
Choosing the right option depends on your performance, budget, and reliability needs.