What is a VPC Endpoint? — Complete Guide for Private AWS Access
Learn what a VPC Endpoint is, why it is used, and how it enables private access to AWS services without using the internet. A complete guide with real-world examples and best practices.
What is a VPC Endpoint? — Complete Guide
When building secure cloud architectures in AWS, one common requirement is accessing AWS services like S3 or DynamoDB without exposing your traffic to the public internet.
That’s exactly what a VPC Endpoint solves.
What is a VPC Endpoint?
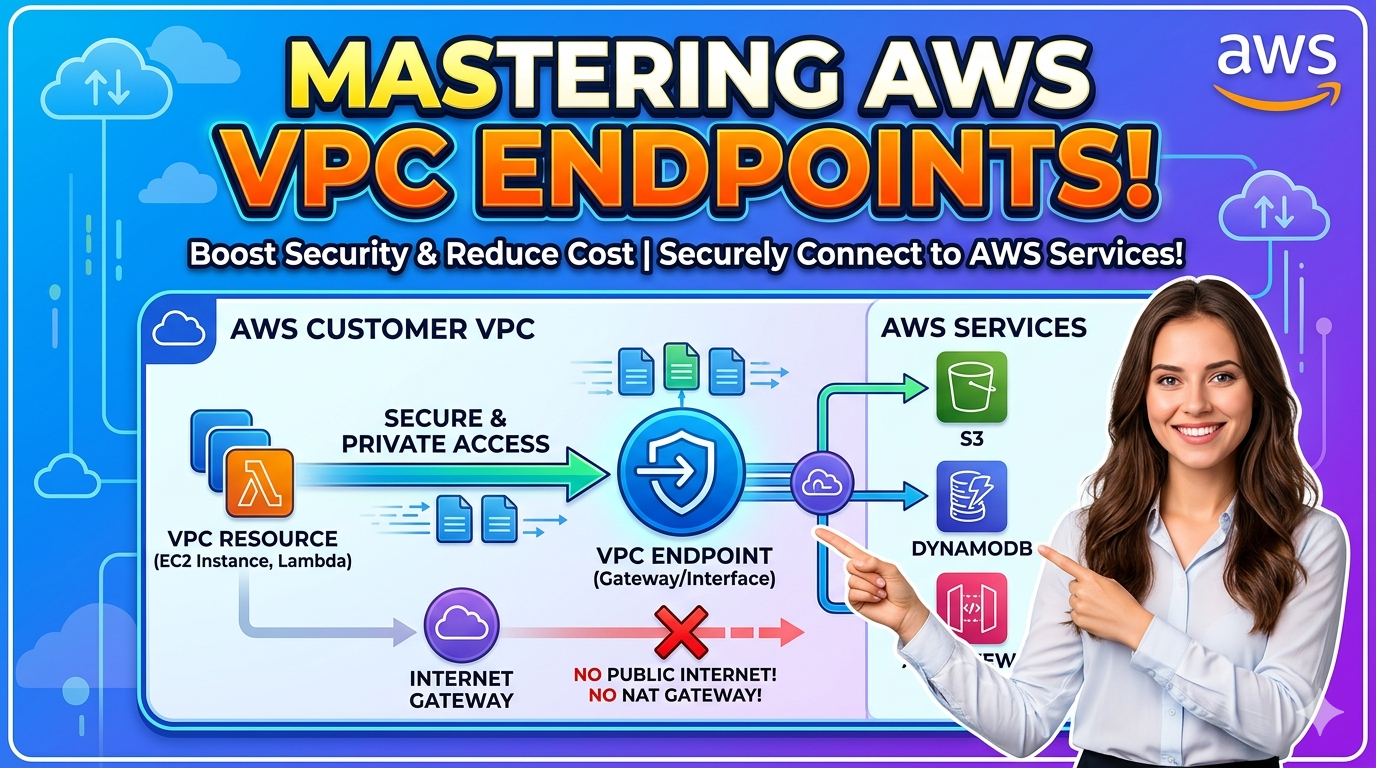
A VPC Endpoint allows you to privately connect your VPC to AWS services without using an Internet Gateway, NAT Gateway, or public IP.
Key Idea:
Keep your traffic inside AWS network — secure and private.
Why Do We Need VPC Endpoint?
Problem:
Without VPC Endpoint:
- Private instances use NAT Gateway to access AWS services
- Traffic goes through the public internet
- Increased cost and security concerns
Solution:
Use VPC Endpoint for private access.
How VPC Endpoint Works
Architecture Flow:
Private EC2 → VPC Endpoint → AWS Service (S3/DynamoDB)
- Traffic never leaves AWS network
- No public exposure
- Highly secure
Types of VPC Endpoints
1. Gateway Endpoint
Used for:
- S3
- DynamoDB
Works via route tables
No additional cost
2. Interface Endpoint (PrivateLink)
Used for:
- Most AWS services (SNS, SQS, EC2 API, etc.)
Creates an Elastic Network Interface (ENI)
Has private IP inside your subnet
Real AWS Example
Scenario:
You have:
- Private EC2 instance
- Need to access S3
Without VPC Endpoint:
- Use NAT Gateway ❌
With VPC Endpoint:
- Direct private connection ✅
Route Table Example (Gateway Endpoint)
Destination: pl-xxxx (S3 Prefix List) → Target: VPC Endpoint
Advantages of VPC Endpoint
- No internet exposure
- Improved security
- Lower latency
- Cost optimization (no NAT usage)
Limitations
- Gateway endpoint only supports S3 & DynamoDB
- Interface endpoints may incur cost
- Requires proper route & DNS configuration
VPC Endpoint vs NAT Gateway
| Feature | VPC Endpoint | NAT Gateway |
|---|---|---|
| Internet Required | ❌ No | ✅ Yes |
| Security | High | Medium |
| Cost | Lower (Gateway type) | Higher |
| Use Case | AWS service access | General internet access |
Best Practices
- Use Gateway Endpoint for S3 whenever possible
- Prefer Interface Endpoint for sensitive services
- Enable private DNS
- Restrict access using endpoint policies
Simple Analogy
Think of it like:
- VPC Endpoint → Private tunnel inside a company network
- NAT Gateway → Going outside via public road
Final Thoughts
VPC Endpoint is essential for building secure AWS systems:
- Keeps traffic private
- Reduces dependency on NAT Gateway
- Improves performance and security